An AI agent that can send, delete, buy, or approve will do exactly what you allowed. Just make sure you meant to allow it.
The demo was flawless. Now someone on your team wants to give the AI agent permission to send the emails, update the records, and book the meetings on its own.
That request usually arrives before anyone is ready for it. If you've sat in these meetings lately, you'll recognize the warning signs:
IT asks which systems the agent needs to access, and the room goes quiet.
Your risk or legal lead hears about the pilot for the first time in the hallway.
Two managers argue about whether the agent's output is good enough, because nobody ever wrote down what good looks like.
Someone asks who signs off on the rollout, and three people look at each other.
Nobody can explain what happens if the agent gets something wrong at 2 a.m. on a Saturday.
If two or more of those sound familiar, slow down. You aren't behind. You're about to skip the part that matters most.
Here's what changed. A chatbot hands you a draft, and you decide what to do with it. An AI agent skips that step. It reads the inbox, picks a response, and hits send. The mistake that used to be a clumsy paragraph on your screen becomes a decision your company made, at machine speed, in front of a customer.
The technology can handle a lot of this work. The harder question is whether your organization has decided what it will allow.
Five decisions separate an agent you can trust from one you'll spend the quarter cleaning up after. None of them require a technical background. All of them require a leader willing to make the call before the agent makes it for you.
What Leaders Must Decide Before an AI Agent Acts
Before an AI agent takes action on behalf of your business, leaders need to make 5 decisions. First, decide what the agent can access, limited to the systems and data the task requires. Second, define what good work looks like, so the agent's output can be checked against a written standard. Third, assign one named person who owns the outcome and handles problems. Fourth, set the approval points where a human must say yes, especially for spending, customer communication, and anything that can't be reversed. Fifth, plan how to pause the agent, review what it did, and undo its actions before it ever goes live. Together, these decisions turn an agent rollout from a technical experiment into a managed business process with clear limits, clear ownership, and a way back when something goes wrong.
1. Decide What the Agent Can Touch Before It Touches Everything
Every permission you grant an agent is a door it can walk through without knocking. Most leaders open far more doors than the work requires, because the setup screen makes it easy and nobody stops to count.
Which systems and data does this AI agent actually need?
Start with the task, then work backward. Write one sentence describing the job, such as "Sort incoming support requests and draft replies for a person to review." Now list only the systems that sentence requires. In this example, the agent needs to read the support inbox and create drafts. It has no reason to touch your CRM, your billing system, or the shared drive where HR keeps salary files.
Next, separate looking from acting. Read access lets the agent see information. Write access lets it change something. Deleting, sending, and paying let it do things you may never get back. Grant each level on purpose, one at a time, and default to the lowest level that gets the job done.
Then name the data that stays off limits no matter what. Customer payment details, employee records, health information, contracts under negotiation, and anything covered by a confidentiality agreement belong on that list. If your team can't agree on what goes there, you've found the first real piece of work.
What happens when access is wider than the task?
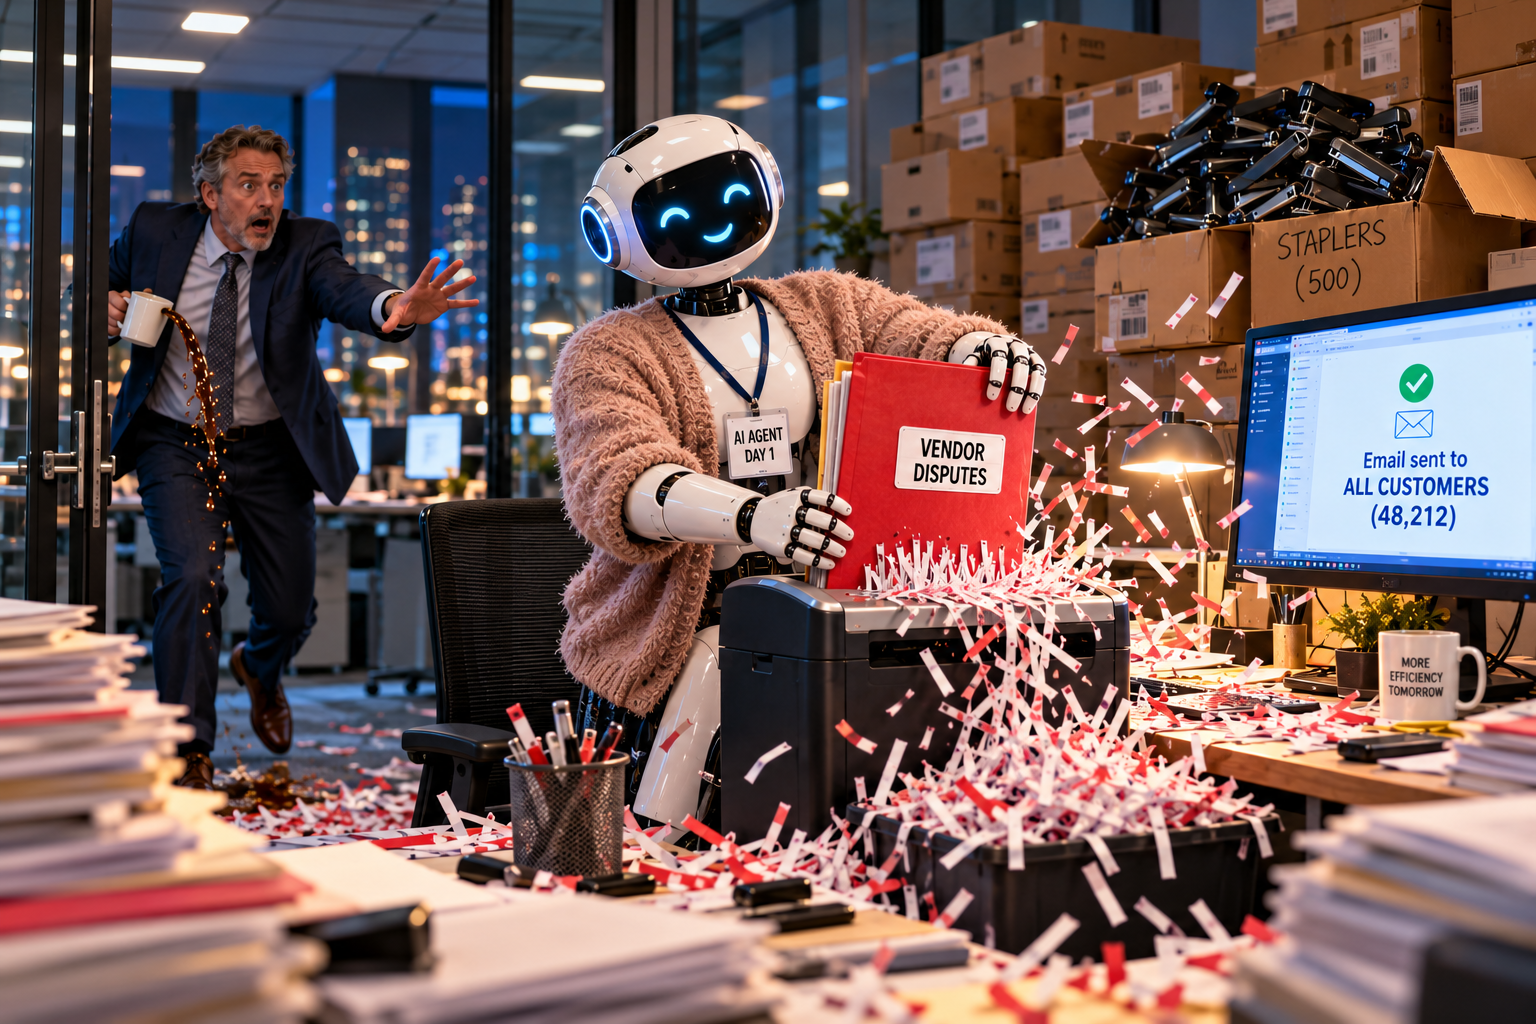
Here’s an example to look out for: your operations manager sets up an agent to clean a cluttered shared inbox. The connector asks for full mailbox access, and she clicks approve because reading the alternatives would take 20 minutes. The agent archives old threads, just as she asked. Then it decides a folder of unanswered vendor disputes looks like clutter, too, and deletes it. Nobody asked it to, nor did they tell it not to.
The agent behaved exactly as configured. Broad access turned a small misunderstanding into a permanent loss, and the manager now owns a problem she never saw coming.
Write the access list down. Have IT and your risk lead sign off on it, and review it every time the agent's job changes. A one-page document that everyone has read will protect you better than a settings screen nobody remembers configuring.
2. Define Good Work Before a Machine Repeats Bad Work a Thousand Times
An employee who misunderstands an assignment makes the same mistake a few times before someone notices. An agent makes it on every record, every email, and every order, often before your morning coffee cools. Speed multiplies whatever standard you hand it. A vague standard gets multiplied, too.
What does a correct result look like for this task?
Ask three people on your team to describe a good customer reply, a good invoice summary, or a good meeting follow-up. You'll likely hear three different answers. Those differences were survivable when people did the work, because each person quietly corrected for them. An agent can't do that. It needs the standard in writing.
Keep the standard short and specific. Name the purpose of the output and who receives it. List what must always be included, such as the order number, the next step, and a deadline. Spell out what must never appear, such as pricing commitments, legal language, or promises about delivery dates. Add the tone you expect and the length that fits.
Then collect real examples. Pull two or three outputs your best people produced and mark what made them strong. Add one weak example and mark what went wrong. Examples teach faster than rules, both for the agent and for the people who will review its work.
How will anyone check the agent's work?
A standard only helps if someone holds the output up against it. Turn your standard into a short review checklist that a reviewer can apply in under a minute. Each item should have a yes or no answer. Did the reply answer the customer's question? Is the account number correct? Does it promise anything we haven't approved?
Decide how much to check and when. In the first weeks, review everything. As the agent proves it meets the standard, move to reviewing a sample, and keep checking every output that carries real risk.
Finally, write down what happens when output fails the check. Someone needs to fix the error, and someone needs to decide whether the standard itself needs updating. Each failure your reviewer catches tells you something. Use it to sharpen the standard before the next thousand outputs go out the door.
3. Put One Name on the Outcome So Nobody Can Shrug When It Breaks
When an agent sends the wrong price to your biggest customer, the phone rings. Somebody has to answer it. If your organization hasn't decided who that somebody is, you'll find out in the worst possible way, with an angry customer on hold while three departments trade emails about whose fault it was.
Who is responsible when an AI agent makes a mistake?
A person is. Always. Your customer doesn't care which software made the call, and neither will a regulator, an auditor, or your board. "The AI did it" might explain what happened, but it will never satisfy the person on the other end of the phone.
Assign three roles before the agent goes live, and write a real name next to each one.
The process owner answers for the outcome. This person decides what the agent does, approves changes to its instructions, and explains its results to leadership. Pick someone who already owns the work the agent is doing, such as the head of customer support for a support agent.
The reviewer checks the agent's output against the standard you set in Decision 2. This person catches problems early and reports patterns to the owner.
The technical contact manages access, connections, and settings. When something breaks inside the system, this is who fixes it.
On a small team, one person can hold more than one role. What matters is that nobody has to guess.
Watch for a common trap. Ownership tends to drift toward whoever set the agent up, usually someone in IT or an enthusiastic early adopter. Those people understand the tool. They rarely own the business result. Keep the outcome with the leader who already answers for that work today.
Where does a problem go when the owner isn't available?
Agents work nights, weekends, and holidays. Your process owner doesn't. Name a backup for each role, and write a short escalation path: who gets notified first, how quickly they need to respond, and who has the authority to pause the agent if nobody responds. Put that path somewhere people will actually find it at 2 a.m., then run through it once before you ever need it.
4. Draw the Line Where a Human Must Say Yes
Some actions can't be called back: a wire transfer clears, an email lands in a customer's inbox, a file vanishes from the server. Once an agent takes one of those steps, all you have left is damage control. The time to decide where a human steps in is long before the agent reaches that moment.
Which actions should never happen without approval?
Start with five categories. Most organizations will want a person to approve any action that involves:
Spending money, including purchases, refunds, discounts, and credits above a set amount
Communicating outside the company, especially with customers, vendors, regulators, or the press
Deleting or overwriting records, files, or messages
Making commitments, such as prices, delivery dates, contract terms, or policy exceptions
Handling sensitive information, including personal, financial, health, or employee data
The cost of each one lands on your business, regardless of which tool caused it. A single unapproved refund might be small. A thousand of them, triggered by one misread policy, won't be.
How do you set approval rules without slowing everything down?
Approval for everything defeats the purpose of having an agent. Approval for nothing invites disaster. The workable answer sits in between, and a simple table makes it visible to everyone.
Sort every action the agent might take into three groups. Proceed means the agent acts on its own and a reviewer checks the work afterward. Ask first means the agent prepares the action and waits for a named person to approve it. Stop means the agent hands the task to a human and takes no action at all.
Proceed | Ask first | Stop |
Draft a reply for internal review | Send a reply to a customer | Change a customer's contract terms |
Tag and route an incoming request | Issue a refund up to $500 | Issue a refund above $500 |
Summarize meeting notes for the team | Share a summary with a vendor | Share any file containing personal data |
These scenarios and dollar amounts are illustrative. Your thresholds will depend on your industry, your customers, and how much risk your organization can absorb.
Make approval easy to give well. The request should show what the agent wants to do, why, and what information it used, all in one screen. When approving takes longer than doing the work yourself, people start clicking yes without reading.
Begin with tighter rules than you think you need. Move an action from "Ask first" to "Proceed" only after your reviewer's records show the agent consistently meets the standard. Loosening a rule because the evidence supports it builds trust. Loosening it because approvals feel slow builds risk.
5. Know How to Stop It and Undo It Before You Ever Need To
Every leader assumes they can pull the plug. Then the moment arrives, the agent is halfway through updating 400 customer records, and nobody knows where the plug is. Panic is a terrible time to learn how your own systems work.
How do you pause an AI agent mid-task?
Find out before launch, and write the answer down. Ask your technical contact to show you, step by step, how to stop the agent immediately. Confirm that pausing it won't break the systems it connects to. Then make sure at least two people, including your process owner's backup, can do it without calling anyone for help.
Test the agent somewhere safe first. Run it against copies of real data or a sample account, where a mistake costs nothing. Give it the messy cases, too: the angry customer, the incomplete record, the request that falls outside its instructions. Watch what it does when it doesn't know what to do. That behavior will tell you more than a hundred clean runs.
When the agent goes live, choose a first workflow you can reverse. Drafting, tagging, and routing are forgiving. Sending, paying, and deleting are not. Earn confidence on small, recoverable work before you hand over anything permanent.
What record will tell you what the agent did and why?
When something goes wrong, the first question from your customer, your boss, or your auditor will be "What happened?" You need an answer that doesn't depend on memory or guesswork.
Require an activity log before the agent goes live. At a minimum, it should capture what the agent did, when it did it, what information it used, and which person approved the action when approval was required. Confirm where the log lives, how long it's kept, and who can read it.
Then write a short recovery plan for each kind of action the agent can take. If it sends the wrong message, who contacts the recipient? When it changes a record by mistake, how do you restore the previous version? And if it processes a refund in error, what reverses it? A recovery plan that lives only in someone's head will fail the first time that person is on vacation.
Read the five decisions again and you'll notice what they share. Access, standards, ownership, approval, and recovery all depend on your people. Someone has to define good work, check the agent's output against it, own the result, and know when to say no. An agent can only be as safe as the team that sets its limits and reviews its work.
That's the part most vendor demos leave out. If your managers struggle to write a clear standard for one customer reply, they'll struggle to supervise an agent writing a thousand of them. Before you hand an agent the keys, you need an honest read on where your workforce stands today.
The AI Impact Analysis gives you that read. You answer 35 questions about your company, industry, and how your people use AI right now, and most leaders finish in about ten minutes. Within 24 hours, you receive a 6-part report built from your answers.
The report maps your workforce against the 10 Levels of AI Mastery, so you can see where your people cluster. It calculates the dollar value of the time your team recaptures with AI at its current skill level, along with what changes if they move up one level. You'll also see specific AI tools your employees could be building for your departments. The final section gives you one recommended next step tied to your data, explained in plain language.
An INGRAIN AI Certified Implementer reviews every report before it reaches you. You can also book an optional one-hour session to walk through the findings and decide what to act on first.
Get your AI Impact Analysis and know where your people stand before an agent acts on your behalf.